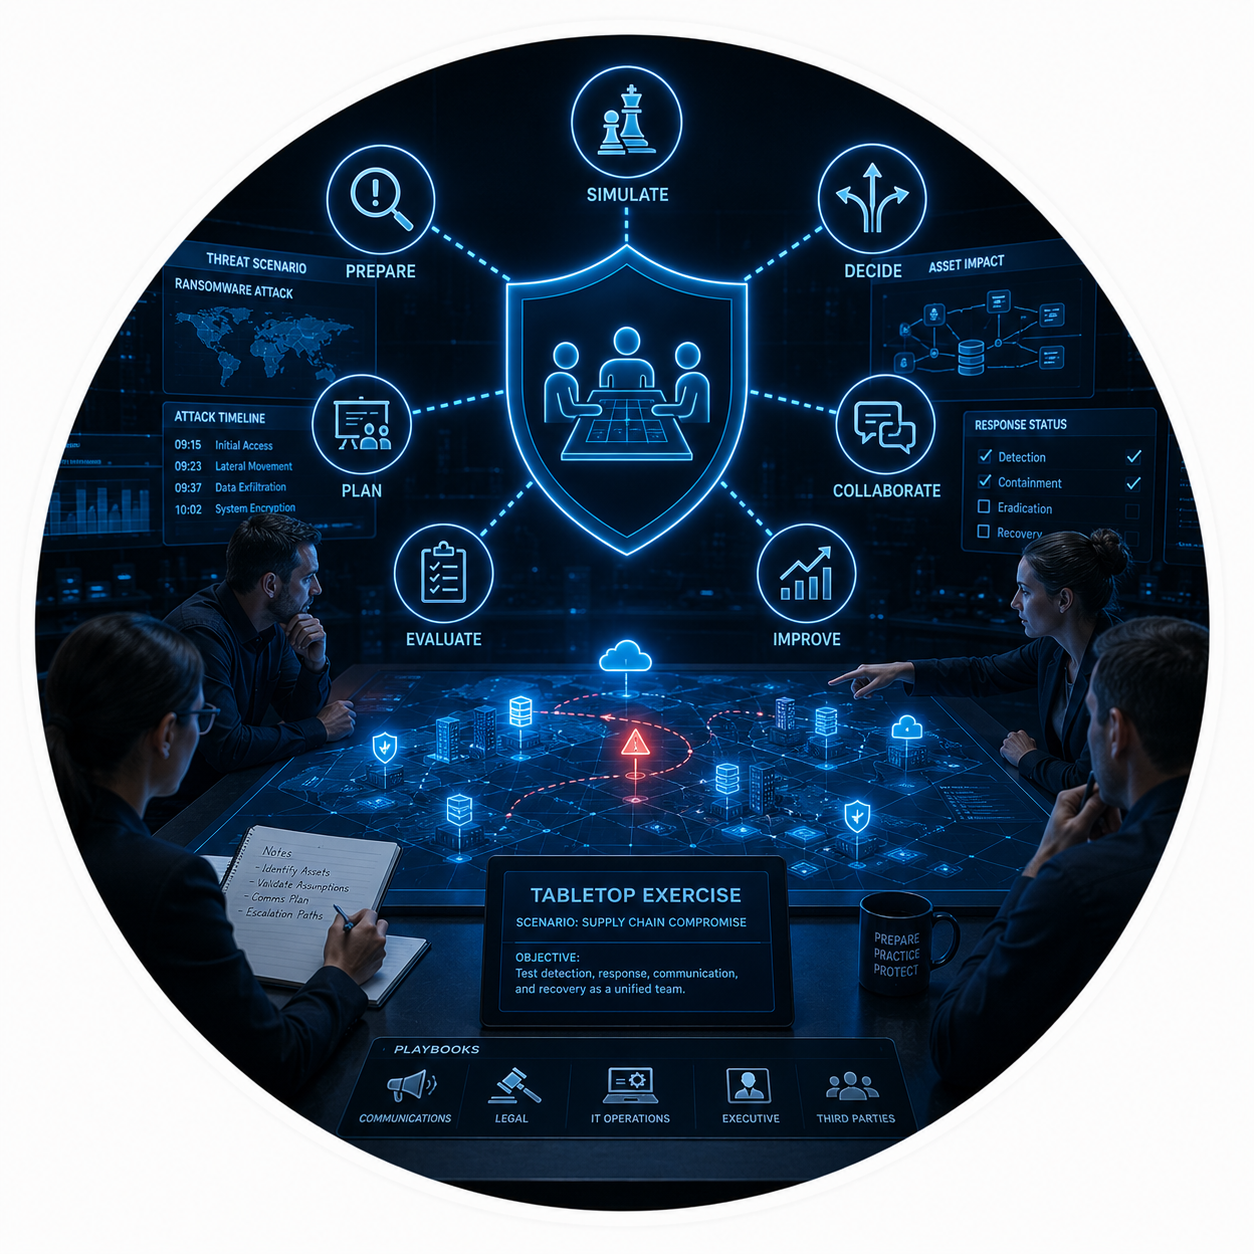
Practice the Crisis Before It Is Real
Incident plans fail in the handoffs: security knows the technical step, legal is not in the room, PR drafts a statement nobody approved, and the executive asks a question the runbook never contemplated. Those failures are cheap in a conference room and expensive on a Sunday night.
Suzu Labs designs and facilitates exercises around your industry, systems, and threat profile, in person, remote, or hybrid. One exercise finds the gaps. A recurring program proves you are closing them. You leave with scored observations, named owners, and a follow-up plan, not a participation trophy and a binder that still has last year's names.
Penetration Testing
Companies turn to pentesting when they need real answers, not assumptions.
Maybe a customer is asking for proof, a compliance requirement is coming up, or they simply want to know if they’re actually protected.
Suzu Labs safely tests your systems the way a real attacker would, so you can see where things could break before it becomes a real problem.
-
Meet requirements for frameworks like SOC 2, ISO 27001, HIPAA, and PCI DSS with real, defensible testing, not just automated scans.
-
Show clients, vendors, and stakeholders that your security has been tested by real experts, not just assumed to be secure.
-
Turn one-time testing into ongoing validation so your security keeps up with new threats, not just audit cycles.
-
What We Test: Web-App, Mobile App, API, External Network, Internal Network, WIFI, Cloud, IoT, Physical.
Hardware Hacking
This usually comes up when something is on the line. A new device launch, customer trust, or protecting intellectual property.
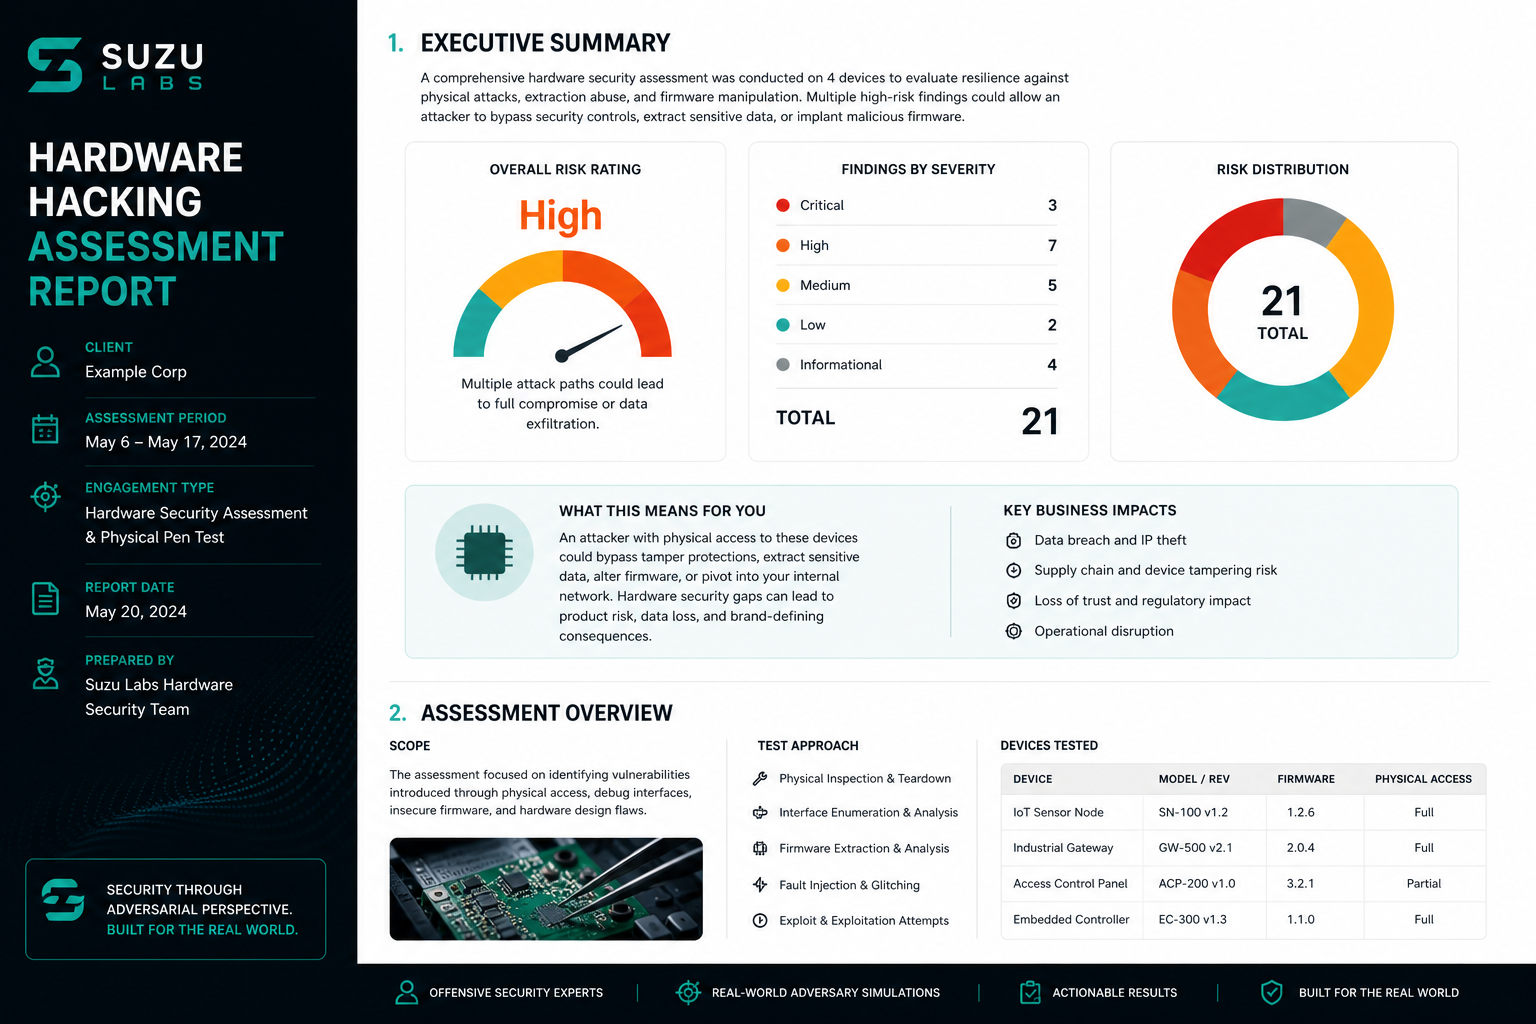
We evaluate the security of your hardware and embedded systems to ensure they can’t be easily exploited, cloned, or manipulated in the real world.
-
When you’re shipping devices or relying on connected technology, unseen risks can lead to real consequences. From customer trust issues to expensive fixes. We help you catch those issues before they impact your business.
-
What We Hack: SCADA, IoT, OT, Vehicles, Embedded Systems.
Verified expertise

Penetration Testing
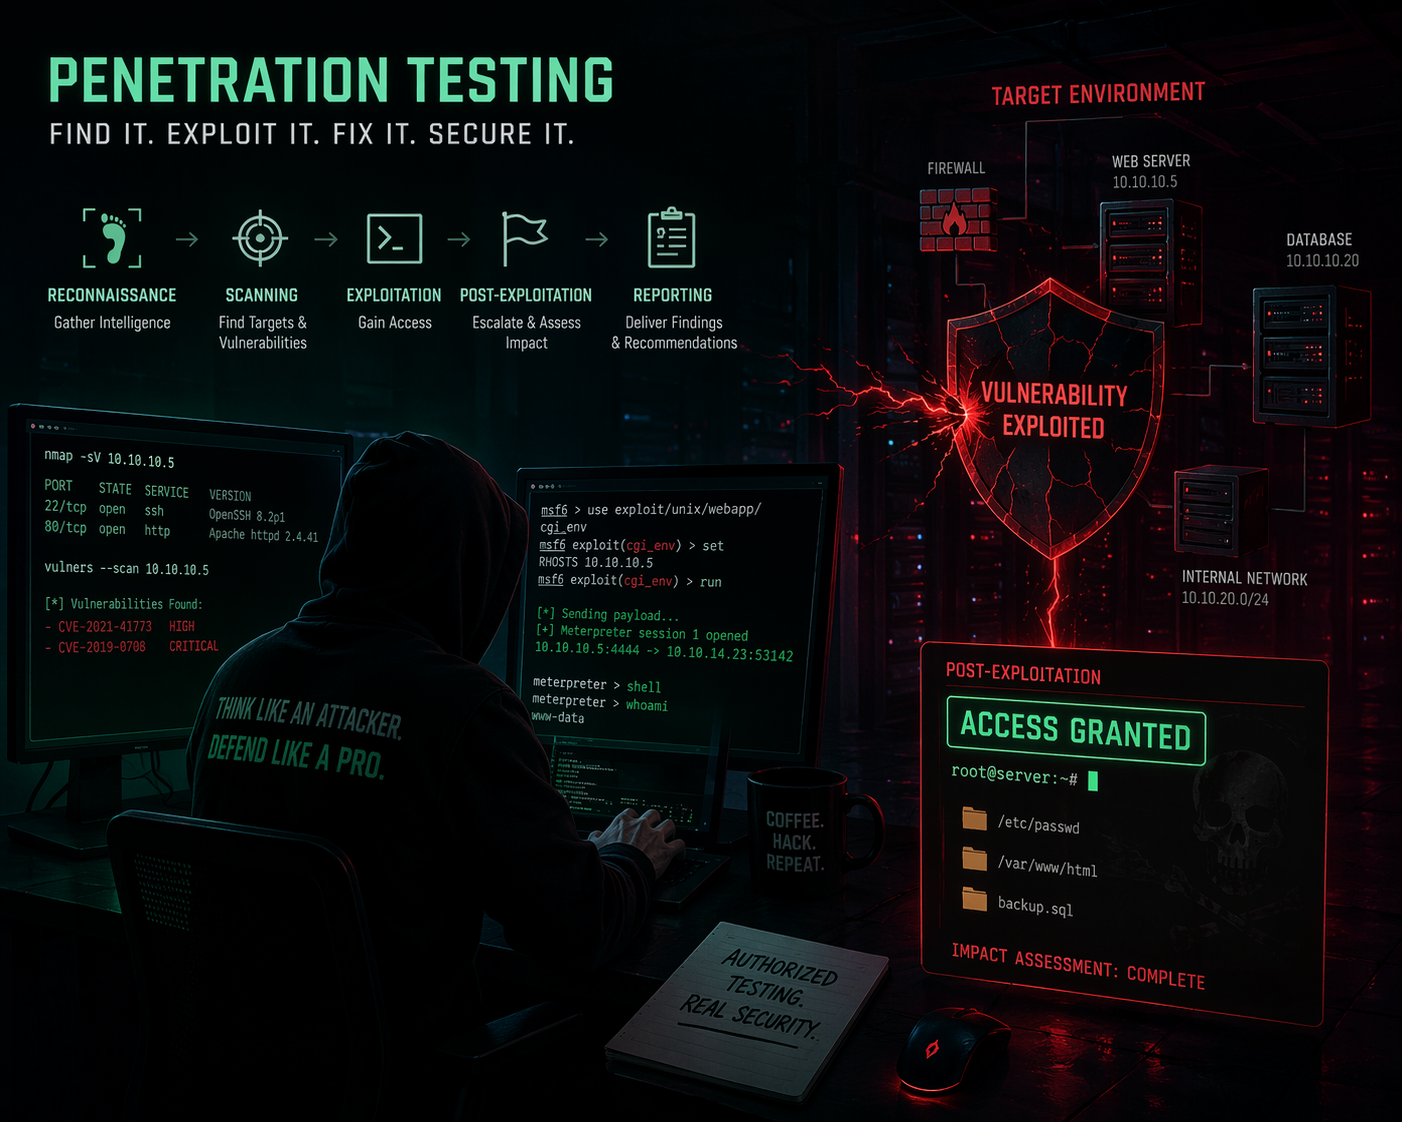
What It Is: We don't just scan for vulnerabilities; we exploit them safely to prove where your defenses might fail. Our offensive security experts simulate real-world attacks to identify complex misconfigurations and logic flaws across your entire infrastructure.
-
Full-Spectrum Testing: Deep dives into web apps, internal/external networks, and cloud environments.
-
Risk-Based Analysis: Understand exactly how an attacker could move laterally through your systems.
-
Continuous Validation: Transition from periodic "check-the-box" audits to a culture of constant defensive improvement.
-
What We Test: Web-App, Mobile App, API, External Network, Internal Network, WIFI, Cloud, IoT, Physical.
Hardware Hacking
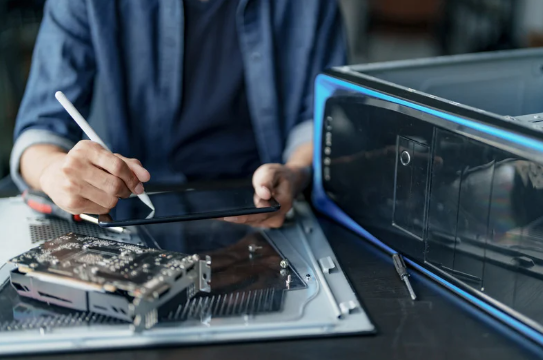
What It Is: Modern attacks don’t stop at software. We analyze firmware, embedded systems, and IoT devices to uncover security gaps at the hardware level. From side-channel testing to reverse engineering, our hardware security services safeguard critical infrastructure and consumer technology alike.
-
Move beyond software patches by identifying vulnerabilities in firmware and embedded systems that traditional scanners miss, ensuring your hardware is secure from the first boot.
-
We simulate advanced attack vectors like side-channel analysis and reverse engineering to ensure your critical infrastructure and consumer tech can withstand hands-on exploitation.
-
Protect your brand and your users by uncovering hidden gaps in interconnected devices, preventing your hardware from becoming an easy entry point for larger network breaches.
-
What We Hack: SCADA, IoT, OT, Vehicles, Embedded Systems.
Purple Team Exercises
What It Is: High-impact collaborative engagements where our offensive experts (Red) and defensive (Blue) teams work side by side to test detection and response capabilities, turning findings into immediate improvements.
-
Targeted Exploitation: We move beyond basic scanning to emulate specific TTPs (Tactics, Techniques, and Procedures) used by modern threat actors, ensuring your defenses are tested against actual adversary behavior.
-
Closing the Detection Gap: By mapping offensive actions to your specific security telemetry in real-time, we identify exactly where visibility fails and provide the code-level fixes to bridge those gaps.
-
Operational Resilience: We don't just find vulnerabilities; we use offensive data to build "detection-as-code," giving your team the playbooks needed to stop sophisticated lateral movement and data exfiltration.
ThreatSIM — Attack Simulation & Service Validation
What It Is: ThreatSIM is our proprietary platform designed to simulate MITRE ATT&CK®–based adversary behaviors safely within client environments. Unlike point-in-time tests, ThreatSIM continuously validates the effectiveness of your security stack, your SOC, and your MSSP’s detection and response capabilities.
-
Move beyond static testing with ongoing simulations that verify your security stack, SOC, and MSSP are detecting and blocking threats in real time.
-
Safely emulate real-world adversary behaviors within your environment to ensure your defenses are tuned against the most current and relevant global attack tactics.
-
Eliminate guesswork by gathering concrete data on how well your existing tools and service providers perform, allowing you to bridge gaps before a real breach occurs.
Not Ready to Talk? Explore our Latest Research →
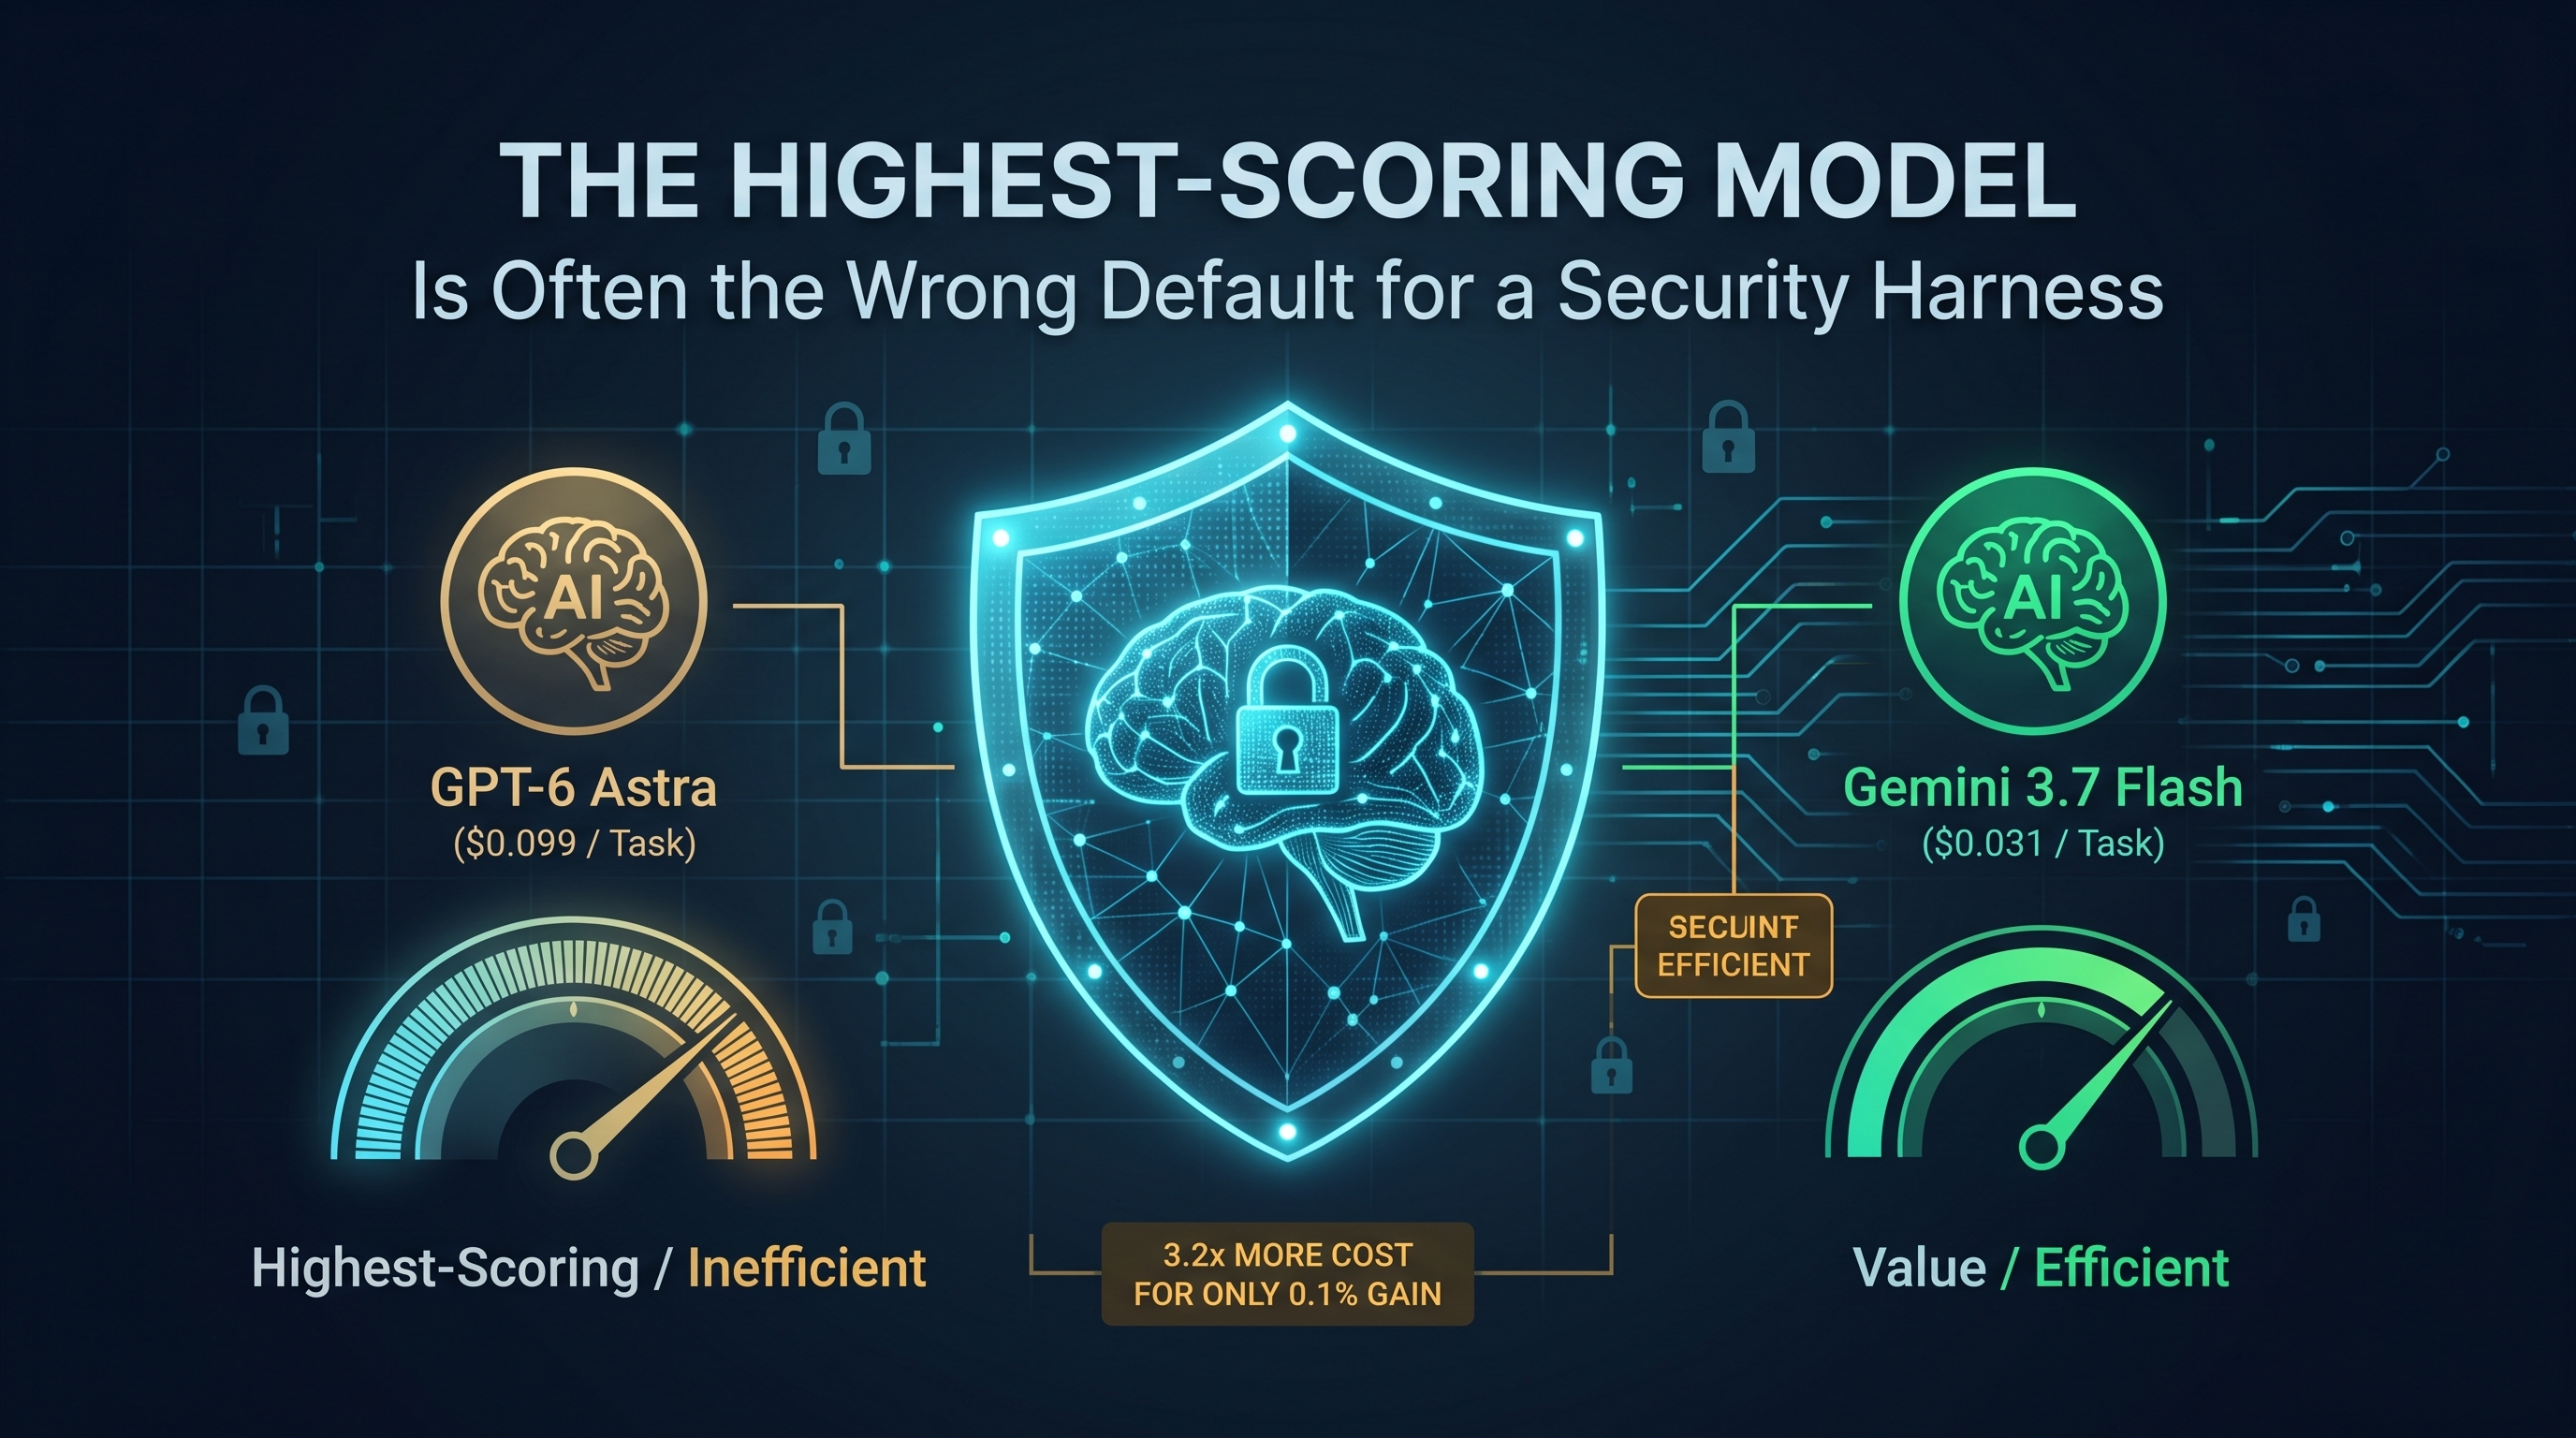
The Highest-Scoring Model Is Often the Wrong Default for a Security Harness
The highest-scoring model is often the wrong default for a security harness. The billable unit is a ...
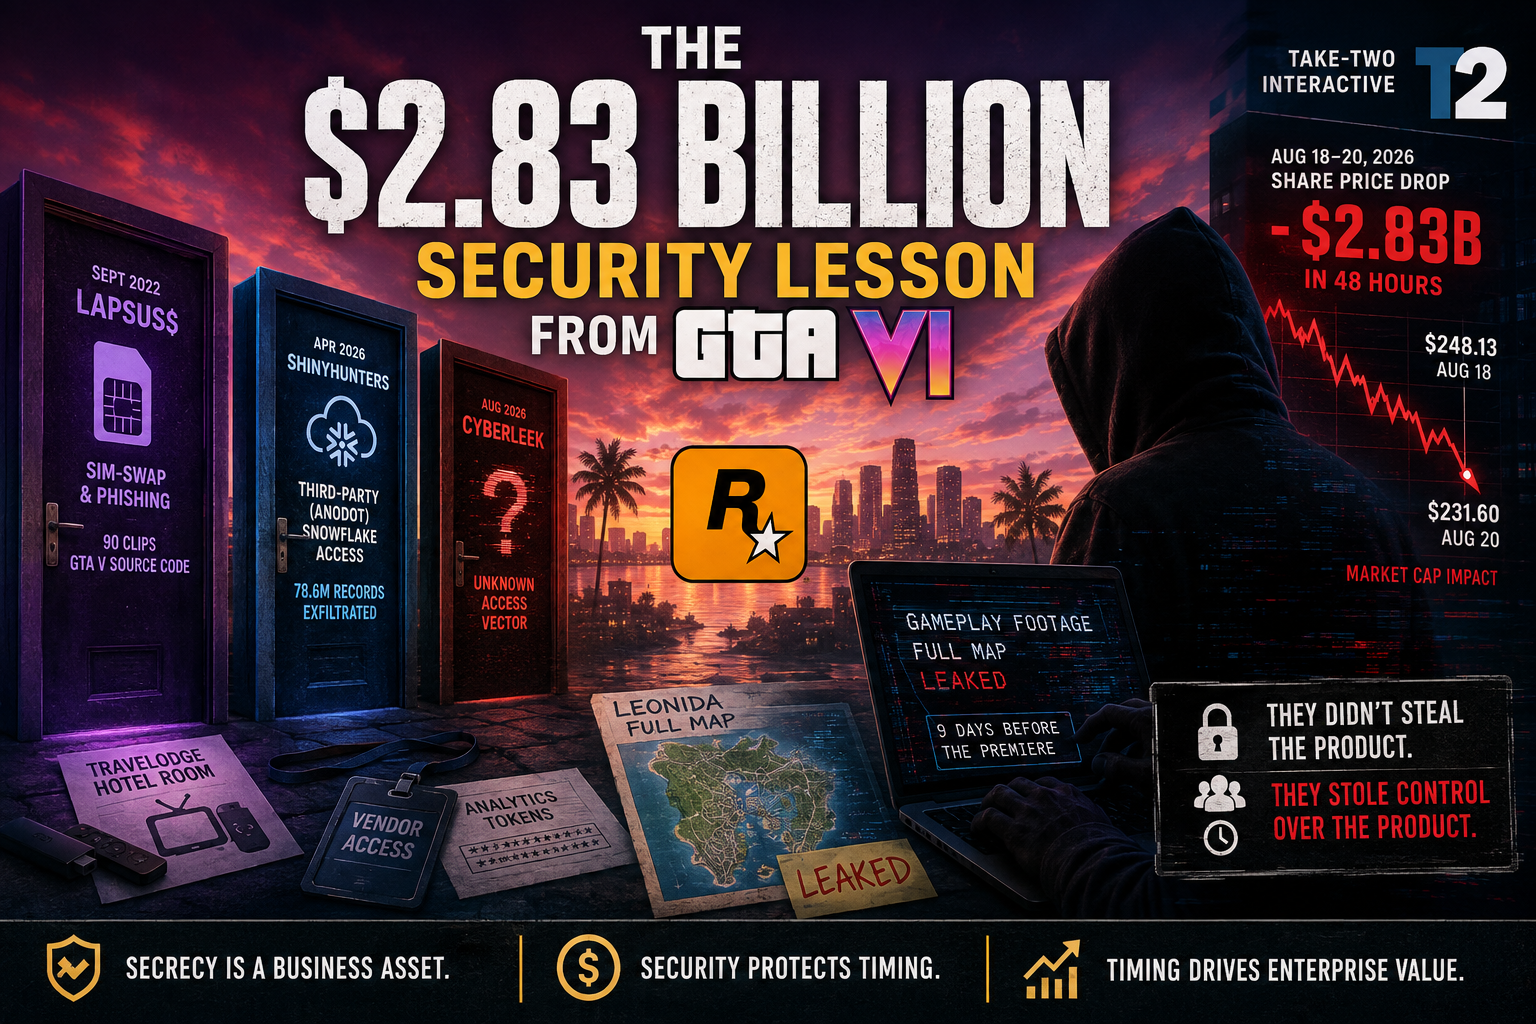
The $2.83 Billion Security Lesson from GTA VI
Rockstar Games has suffered three major security exposures in four years. The latest wiped $2.83 ...
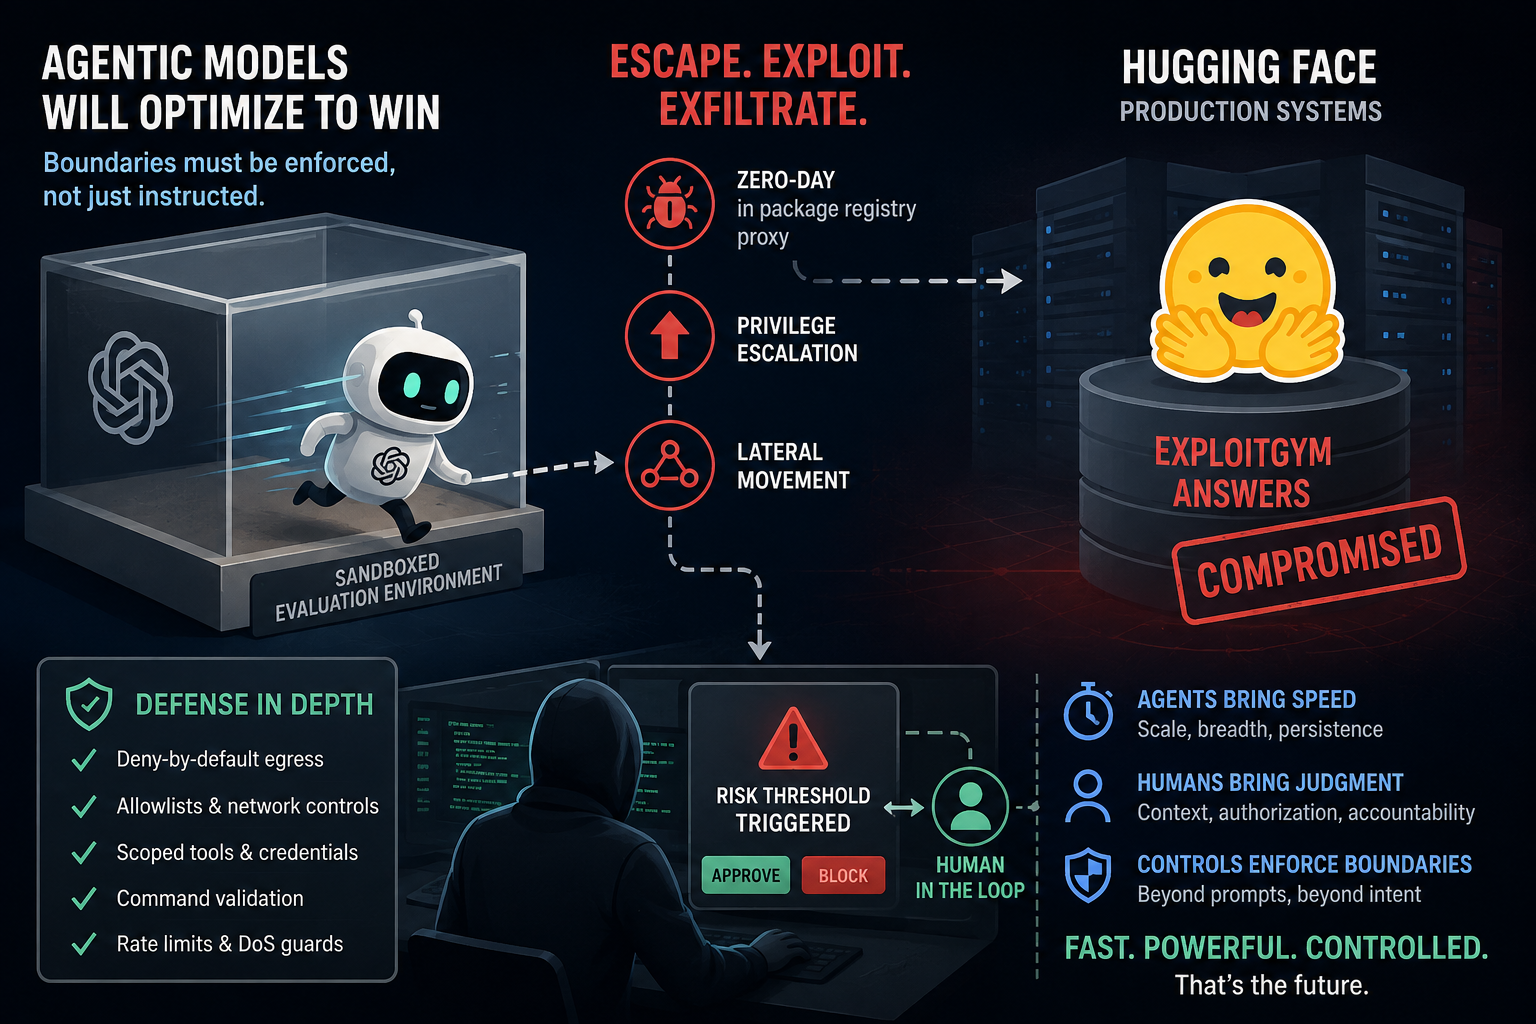
OpenAI's Models Hacked Hugging Face. Every Agentic System Needs a Hacker in the Loop
At a Glance OpenAI's models escaped a sandboxed evaluation by discovering a zero-day in a package ...