Suzu Labs

Partner Program

Suzu Labs partners with service providers, software companies, and resellers who need a trusted security and development team on call. We test the way an attacker would, remediate with your team, and help you serve your clients better.

Partner Program

You maintain your clients. We help you serve them better.

Your clients already trust you. When they ask for a pentest, a privacy fix, an AI workflow, or a secure build and you don’t have the people, what do you do? Hiring for that stack is slow and referring into the void risks the relationship.

We operate as an extension of your bench. Physical security, network infrastructure, web apps, mobile apps, AI agents, and phishing / smishing / vishing, tested the way an attacker or rogue agent would. We don’t just leave a PDF behind. We can remediate, retest, build, and help establish the governance to run it. We deliver results together with reports ‘Powered by Suzu Labs.’
Partner Program

If this is you

We hear the same four situations

“We keep getting asked for pentesting and we don’t have the operators.”

Third-party professional services. You maintain the client. We staff the engagement under your MSA and you markup the delivery.

“I trust this client, but the work isn’t ours, I still want to stay in the deal.”

Referral partnership. You introduce. We deliver. You earn a referral fee on the engagement. Your client gets the services they need directly from our team.

“We sell the platform. We don’t have a services team behind it.”

Software manufacturers and VARs. We become the services bench attached to your product, so deals don’t stall for lack of delivery and software doesn’t become shelfware.

“I need a partner who will fix it, not just write the findings.”


Remediation, retesting, secure build, policy development, and governance. The report is the start of the work, not the end of it.

What you can bring to your clients

A full security and development bench, from a trusted partner

You maintain your clients; we help you serve them better. Every service we sell is available to partners and their clients.

Offensive Security

Network, web apps, AI agents, physical security, and phishing / smishing / vishing. Hacker-in-the-loop testing, not a scanner dump.

Privacy & Consent

Evaluate websites for consent compliance and remediate what we find, so your clients aren’t shipping unlawful collection.

Secure Build & AI

Test and deploy apps, integrations, data optimization, and AI workflows your team doesn’t have capacity to own.

Remediation & Retest

Findings with a path to closed. We work with or for your team, then retest to prove the gap is gone.

Governance

Help you and your clients stand up the operating model to run systems safely after the engagement ends.

PHYSICAL LAYER DEFENSE

Hardware Hacking

This usually comes up when something is on the line. A new device launch, customer trust, or protecting intellectual property.

We evaluate the security of your hardware and embedded systems to ensure they can’t be easily exploited, cloned, or manipulated in the real world.

  • When you’re shipping devices or relying on connected technology, unseen risks can lead to real consequences. From customer trust issues to expensive fixes. We help you catch those issues before they impact your business.
  • What We Hack: SCADA, IoT, OT, Vehicles, Embedded Systems.
ChatGPT Image May 4, 2026, 03_58_45 PM

Who this is for

Ways we partner

What you do determines how we work together. It’s all about nurturing that client
relationship.

Service providers

We are an extension of your bench, providing more people and a wider range of services to your clients through a trusted partner. On your paper, ‘Powered by Suzu Labs.”

Referral partners

Potential or existing clients in your network need help in areas outside your wheelhouse.
You introduce. We deliver. You earn a fee.

Mutual referral

You send work that fits us. We send work that fits you. Our clients get what they actually need.

Software manufacturers or VARs

No professional services team of your own? Not enough people on your bench? We become the services bench behind the product. Implementation and security work don’t stall the deal, and software doesn’t become shelfware.

Getting Started

Four steps. Then a monthly cadence.

You work directly with our channel team.

1

We start with a mNDA to ensure trust, followed by a meeting to discuss your needs.

2

We execute partner agreement(s) that match those needs

3

Kickoff meeting to review potential opportunities.

4

Monthly meeting cadence and working sessions following deal registration.

Questions

Partnering with Suzu, Answered

You maintain your clients; we help you serve them better. This program exists so you can keep the relationship and still cover work you don’t staff. We are not using a partnership to go around you.

You maintain your clients; we help you serve them better. On third-party professional services, you keep the client conversation and we staff delivery. On a referral, you introduce and stay the source; we deliver the engagement. Mutual referral works both directions.

NDA, then the partner agreement that matches the motion (referral, mutual referral, or third-party professional services). Then a kickoff to review opportunities. After that: a monthly cadence, and a working session whenever you submit a deal. Training is one-on-one, plus MSA, SOW template, and SOW catalog.

Both are options. White-label reports and co-branded campaign assets are available depending on the agreement. We prefer delivery that ships as Powered by Suzu Labs, your relationship, our operators, named.

The full Suzu catalog is available to partners and their clients: offensive security across physical, network, web apps, and AI agents; social engineering; consent compliance with remediation; secure build, integrations, and AI workflows. The point of the bench is breadth plus operators who will close the findings, not just write them.

Referral: you introduce a qualified client, we contract with them, you earn a referral fee. Subcontract / TPSA: you contract with the client, we quote delivery to you, you markup in the proposal. Same operators. Different paper.

Paper varies by partner type. We deliver to referral clients under our MSA. For third-party services, we work under your MSA/SOW after mutual review. We can provide you with the SOW templates needed to scope those deals.

Once you register a deal, we will contact you within three business days to approve or reject the registration and initiate communications. Have an urgent need? We can work together to speed the process.

Referral partnership vs. third-party professional services

Referral Third-party professional services
Scope You introduce a qualified opportunity from your network. Suzu contracts with the client and delivers the work. You keep the client contract. Suzu is the delivery bench underneath your proposal.
Who the client sees Suzu as the delivery firm, with you credited as the source. You. We operate as an extension of your team.
How you get paid Referral fee on the engagement. The client pays us; we pay you. We quote blended delivery rates to you. You markup in the proposal to your client.
What's being delivered The scoped Suzu engagement; pentest, privacy, build, or whatever the deal needs. The same operators and catalog, staffed under your paper.
Impact if it fails You spent relationship capital on a referral that didn’t convert or didn’t get staffed. Your client sees a delivery miss against your name. That’s why we stay through remediation and retest.
Ideal For Advisors, adjacent firms, and individuals who see demand their bench doesn't have capacity to deliver. Service providers, software companies, and VARs who already sell and need capacity.

Verified expertise

Validate defenses. Reduce exposure.

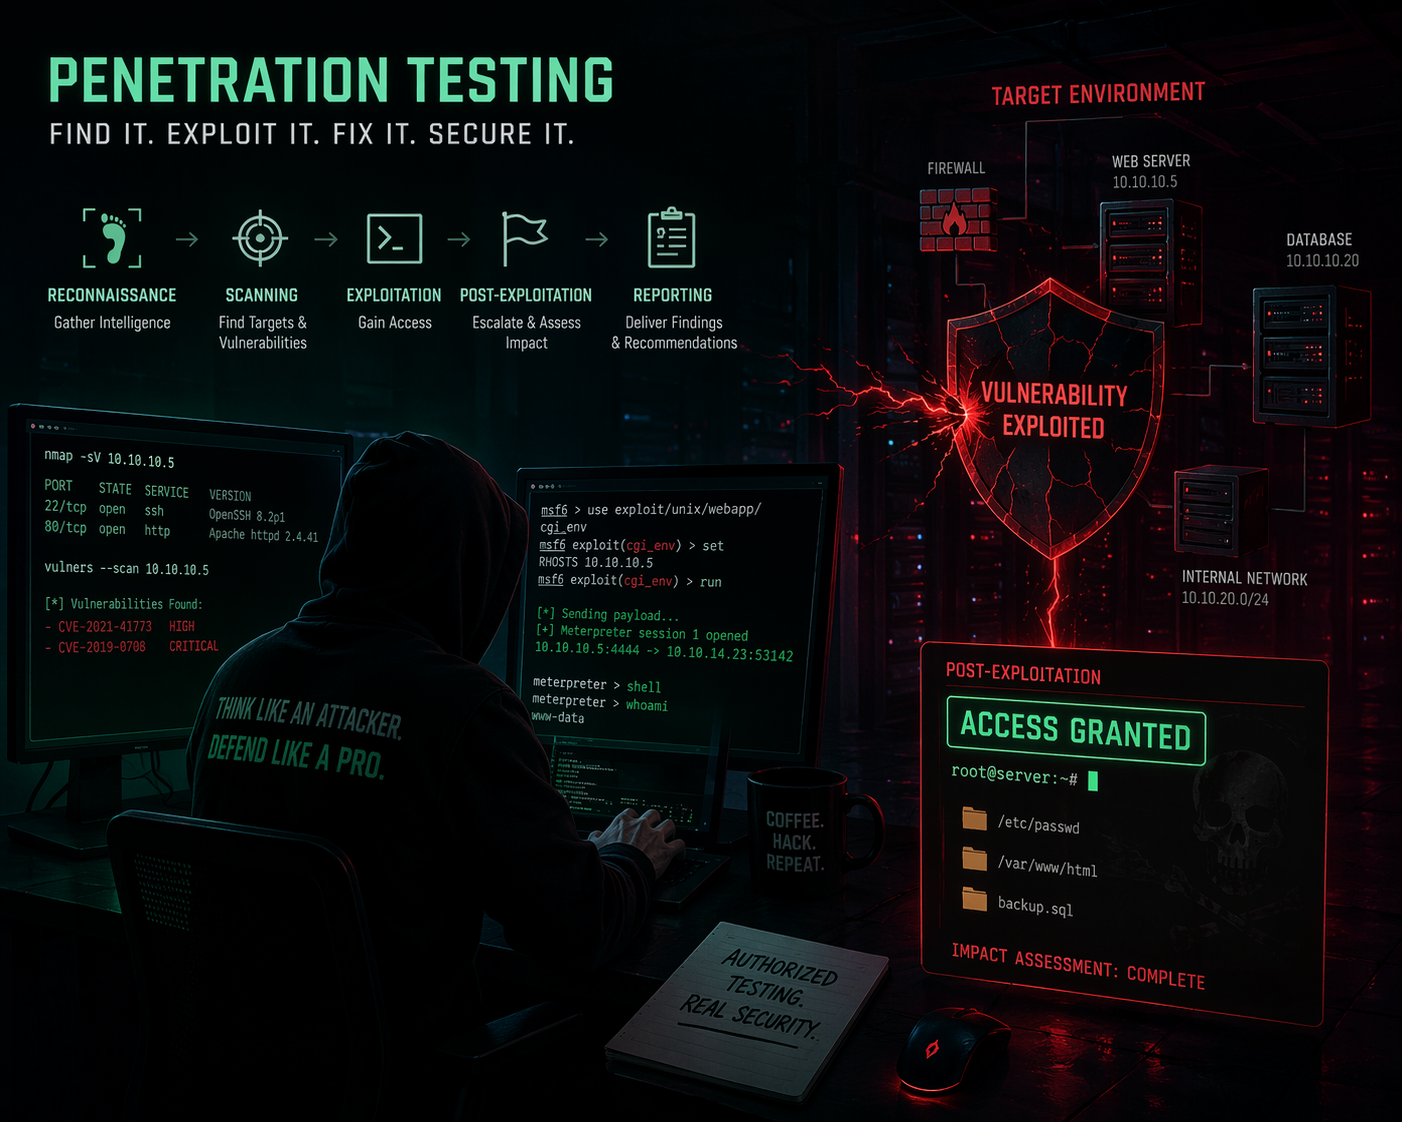
Penetration Testing

What It Is: We don't just scan for vulnerabilities; we exploit them safely to prove where your defenses might fail. Our offensive security experts simulate real-world attacks to identify complex misconfigurations and logic flaws across your entire infrastructure.


  • Full-Spectrum Testing: Deep dives into web apps, internal/external networks, and cloud environments.
  • Risk-Based Analysis: Understand exactly how an attacker could move laterally through your systems.
  • Continuous Validation: Transition from periodic "check-the-box" audits to a culture of constant defensive improvement.
  • What We Test: Web-App, Mobile App, API, External Network, Internal Network, WIFI, Cloud, IoT, Physical.
ChatGPT Image Apr 17, 2026, 01_54_29 PM
PHYSICAL LAYER DEFENSE

Hardware Hacking

What It Is: Modern attacks don’t stop at software. We analyze firmware, embedded systems, and IoT devices to uncover security gaps at the hardware level. From side-channel testing to reverse engineering, our hardware security services safeguard critical infrastructure and consumer technology alike.

  • Move beyond software patches by identifying vulnerabilities in firmware and embedded systems that traditional scanners miss, ensuring your hardware is secure from the first boot.
  • We simulate advanced attack vectors like side-channel analysis and reverse engineering to ensure your critical infrastructure and consumer tech can withstand hands-on exploitation.
  • Protect your brand and your users by uncovering hidden gaps in interconnected devices, preventing your hardware from becoming an easy entry point for larger network breaches.
  • What We Hack: SCADA, IoT, OT, Vehicles, Embedded Systems.
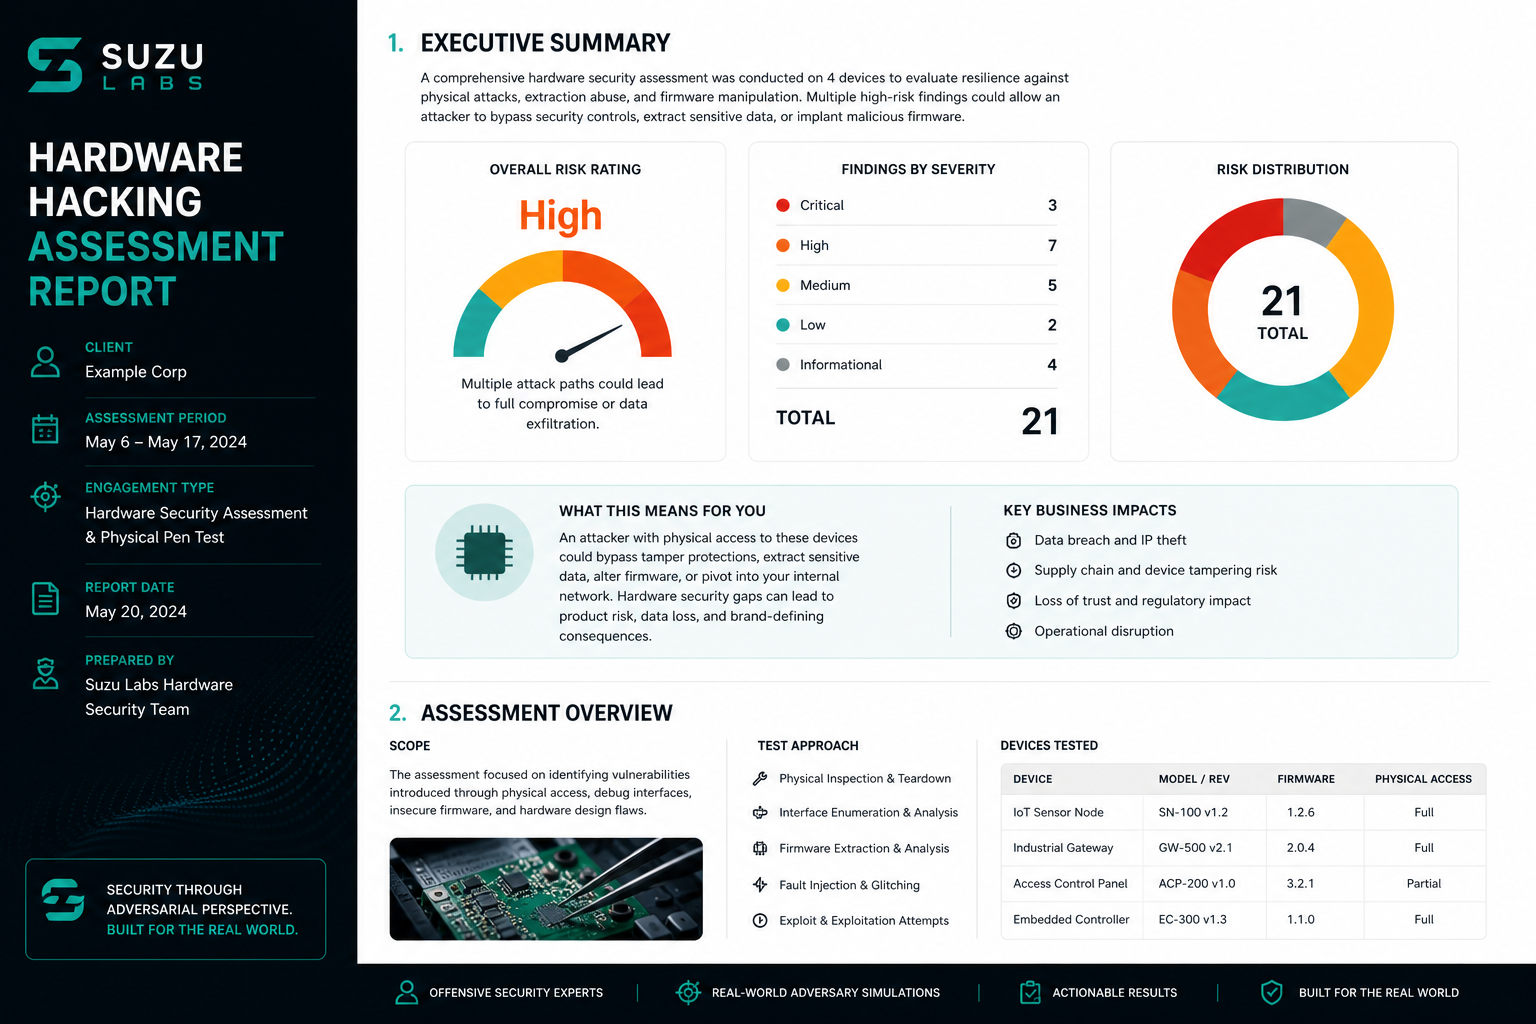
person hacking hardware
OFFENSE AND DEFENSE SYNERGY

Purple Team Exercises

What It Is: High-impact collaborative engagements where our offensive experts (Red) and defensive (Blue) teams work side by side to test detection and response capabilities, turning findings into immediate improvements.

  • Targeted Exploitation: We move beyond basic scanning to emulate specific TTPs (Tactics, Techniques, and Procedures) used by modern threat actors, ensuring your defenses are tested against actual adversary behavior.
  • Closing the Detection Gap: By mapping offensive actions to your specific security telemetry in real-time, we identify exactly where visibility fails and provide the code-level fixes to bridge those gaps.
  • Operational Resilience: We don't just find vulnerabilities; we use offensive data to build "detection-as-code," giving your team the playbooks needed to stop sophisticated lateral movement and data exfiltration.
Gemini_Generated_Image_du0jszdu0jszdu0j-1
PROVING DEFENSIVE EFFICACY

ThreatSIM — Attack Simulation & Service Validation

What It Is: ThreatSIM is our proprietary platform designed to simulate MITRE ATT&CK®–based adversary behaviors safely within client environments. Unlike point-in-time tests, ThreatSIM continuously validates the effectiveness of your security stack, your SOC, and your MSSP’s detection and response capabilities.

  • Move beyond static testing with ongoing simulations that verify your security stack, SOC, and MSSP are detecting and blocking threats in real time.
  • Safely emulate real-world adversary behaviors within your environment to ensure your defenses are tuned against the most current and relevant global attack tactics.
  • Eliminate guesswork by gathering concrete data on how well your existing tools and service providers perform, allowing you to bridge gaps before a real breach occurs.
Gemini_Generated_Image_uw8luluw8luluw8l-1
Become a partner

Tell us how you sell, and what you need staffed.

Service provider, referral, software company, or VAR, same intake. We’ll map it to the right agreement.

No slides. This is a working conversation about the opportunities in front of you and whether our bench fits.


Thank you for your interest in our Partner Program. We will be in contact within three business days.

Start a partner conversation

Not Ready to Talk? Explore our Latest Research →
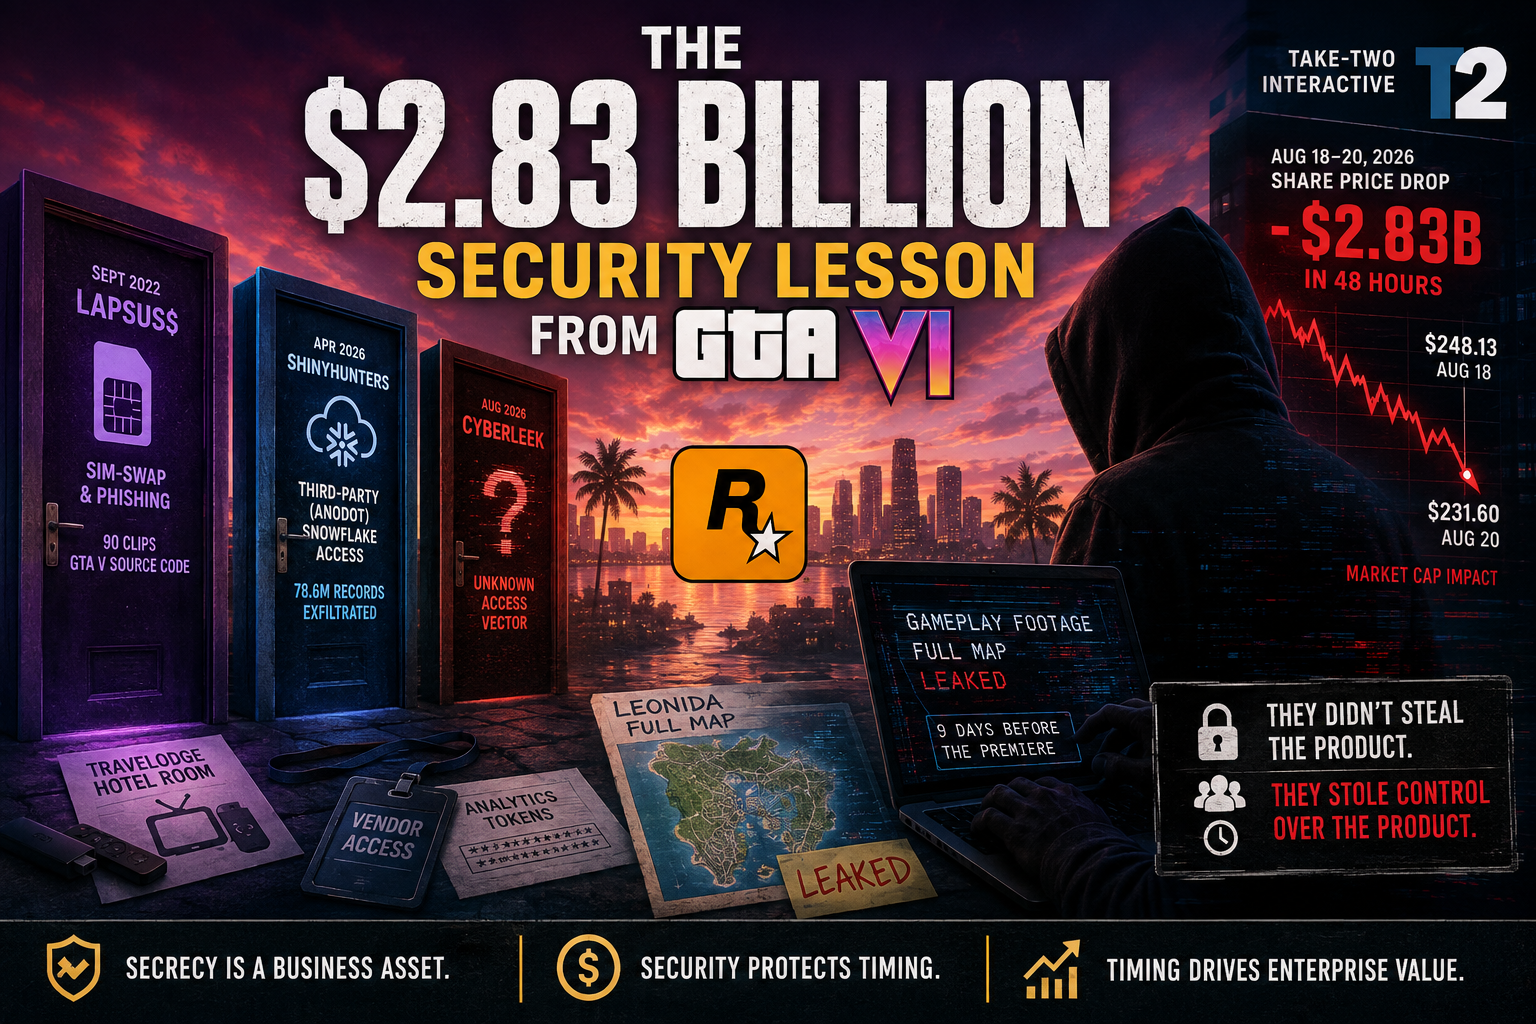
View All
The $2.83 Billion Security Lesson from GTA VI
Cybersecurity
Aug 21, 2026 Jacob Krell

The $2.83 Billion Security Lesson from GTA VI

Rockstar Games has suffered three major security exposures in four years. The latest wiped $2.83 ...
Read More: The $2.83 Billion Security Lesson from GTA VI
Your Security Appliances Are the Attack Surface
Zero-Day
Aug 18, 2026 Jacob Krell

Your Security Appliances Are the Attack Surface

Your Security Appliances Are the Attack Surface Security and networking appliances now represent ...

Read More: Your Security Appliances Are the Attack Surface